Security reviews that keep pace with engineering.

Security review becomes part of how engineering already works, from the first scoping ticket to the final fix.
Book a Demo
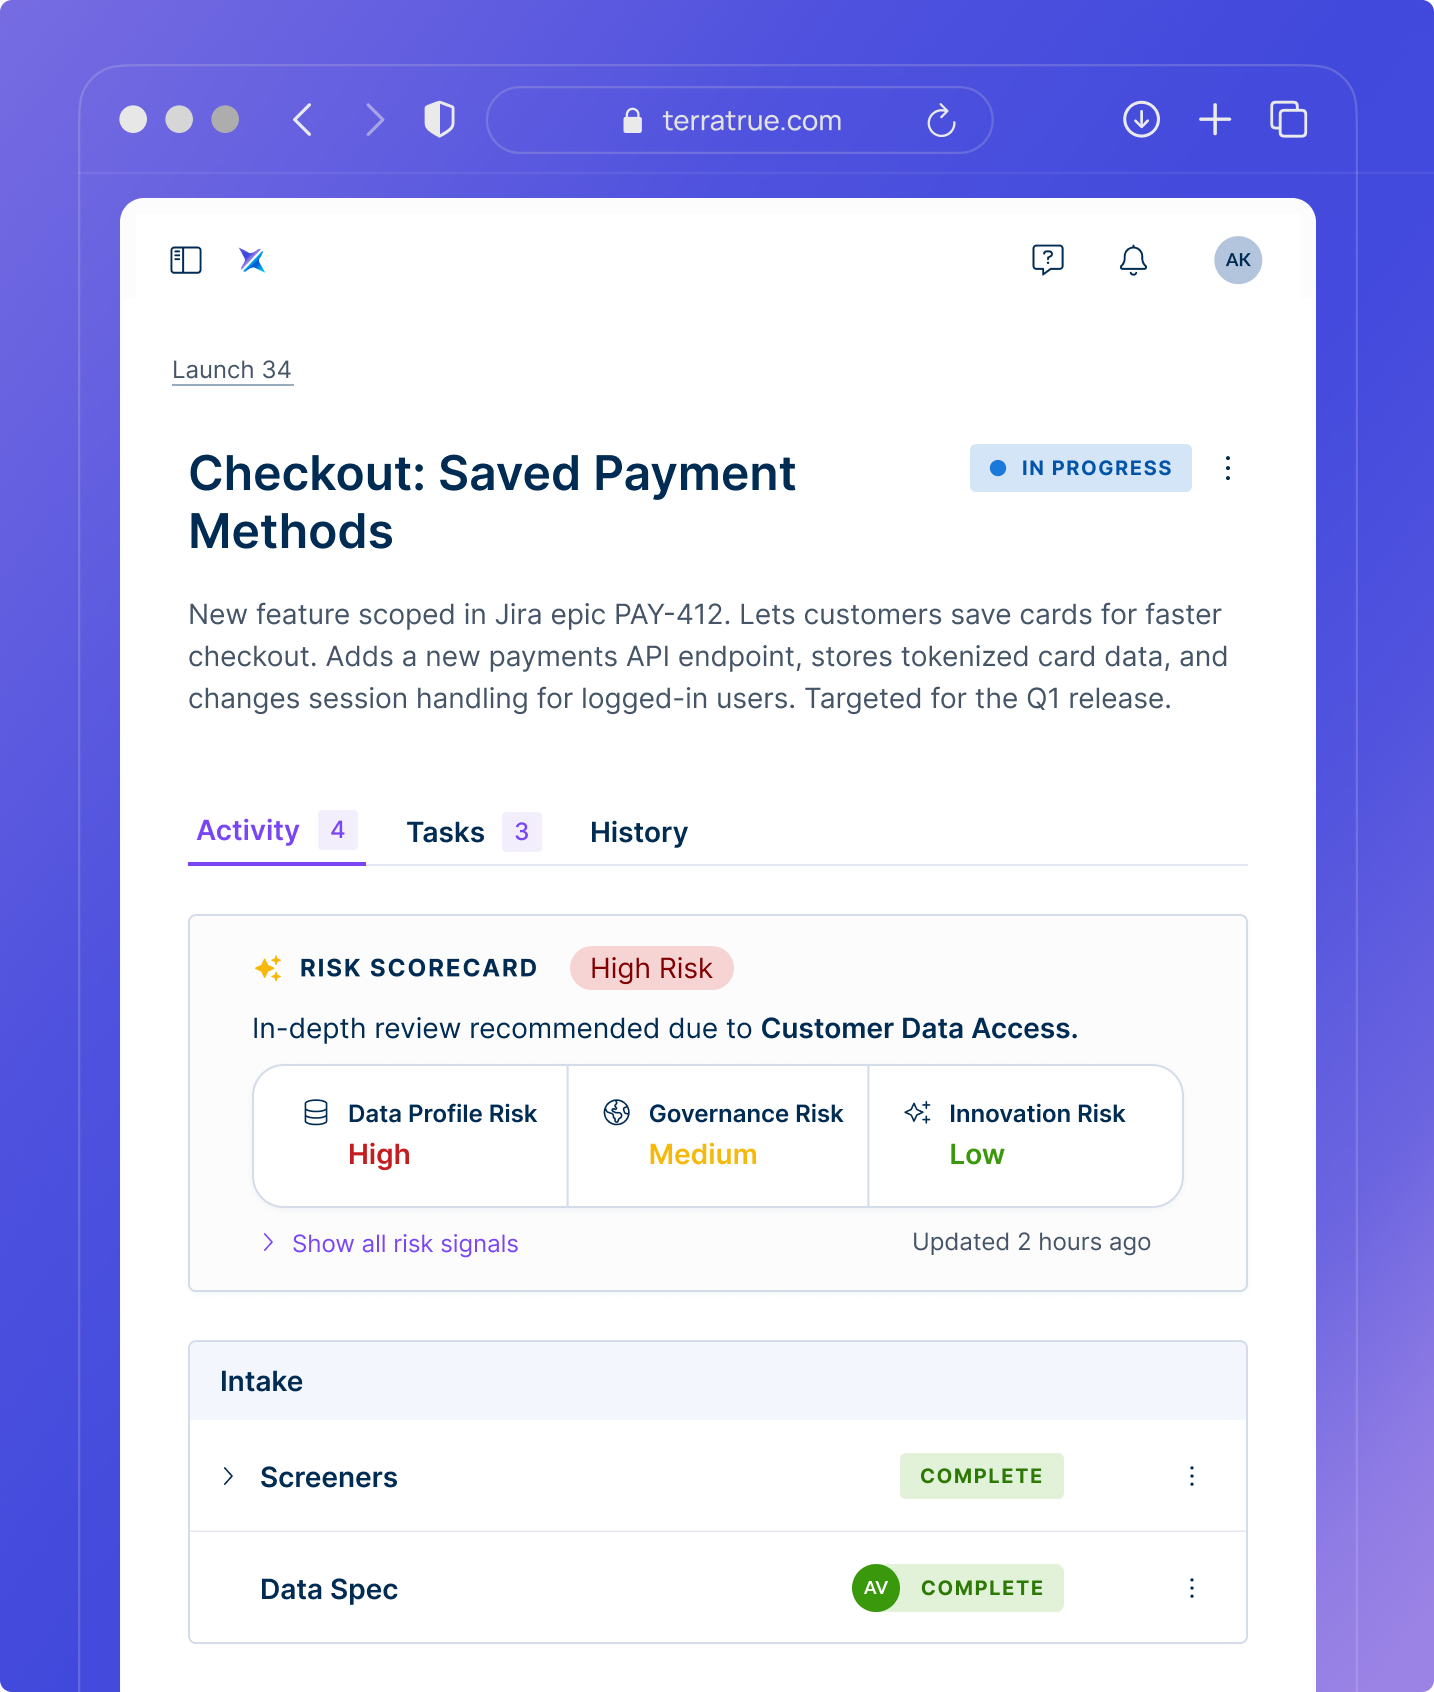
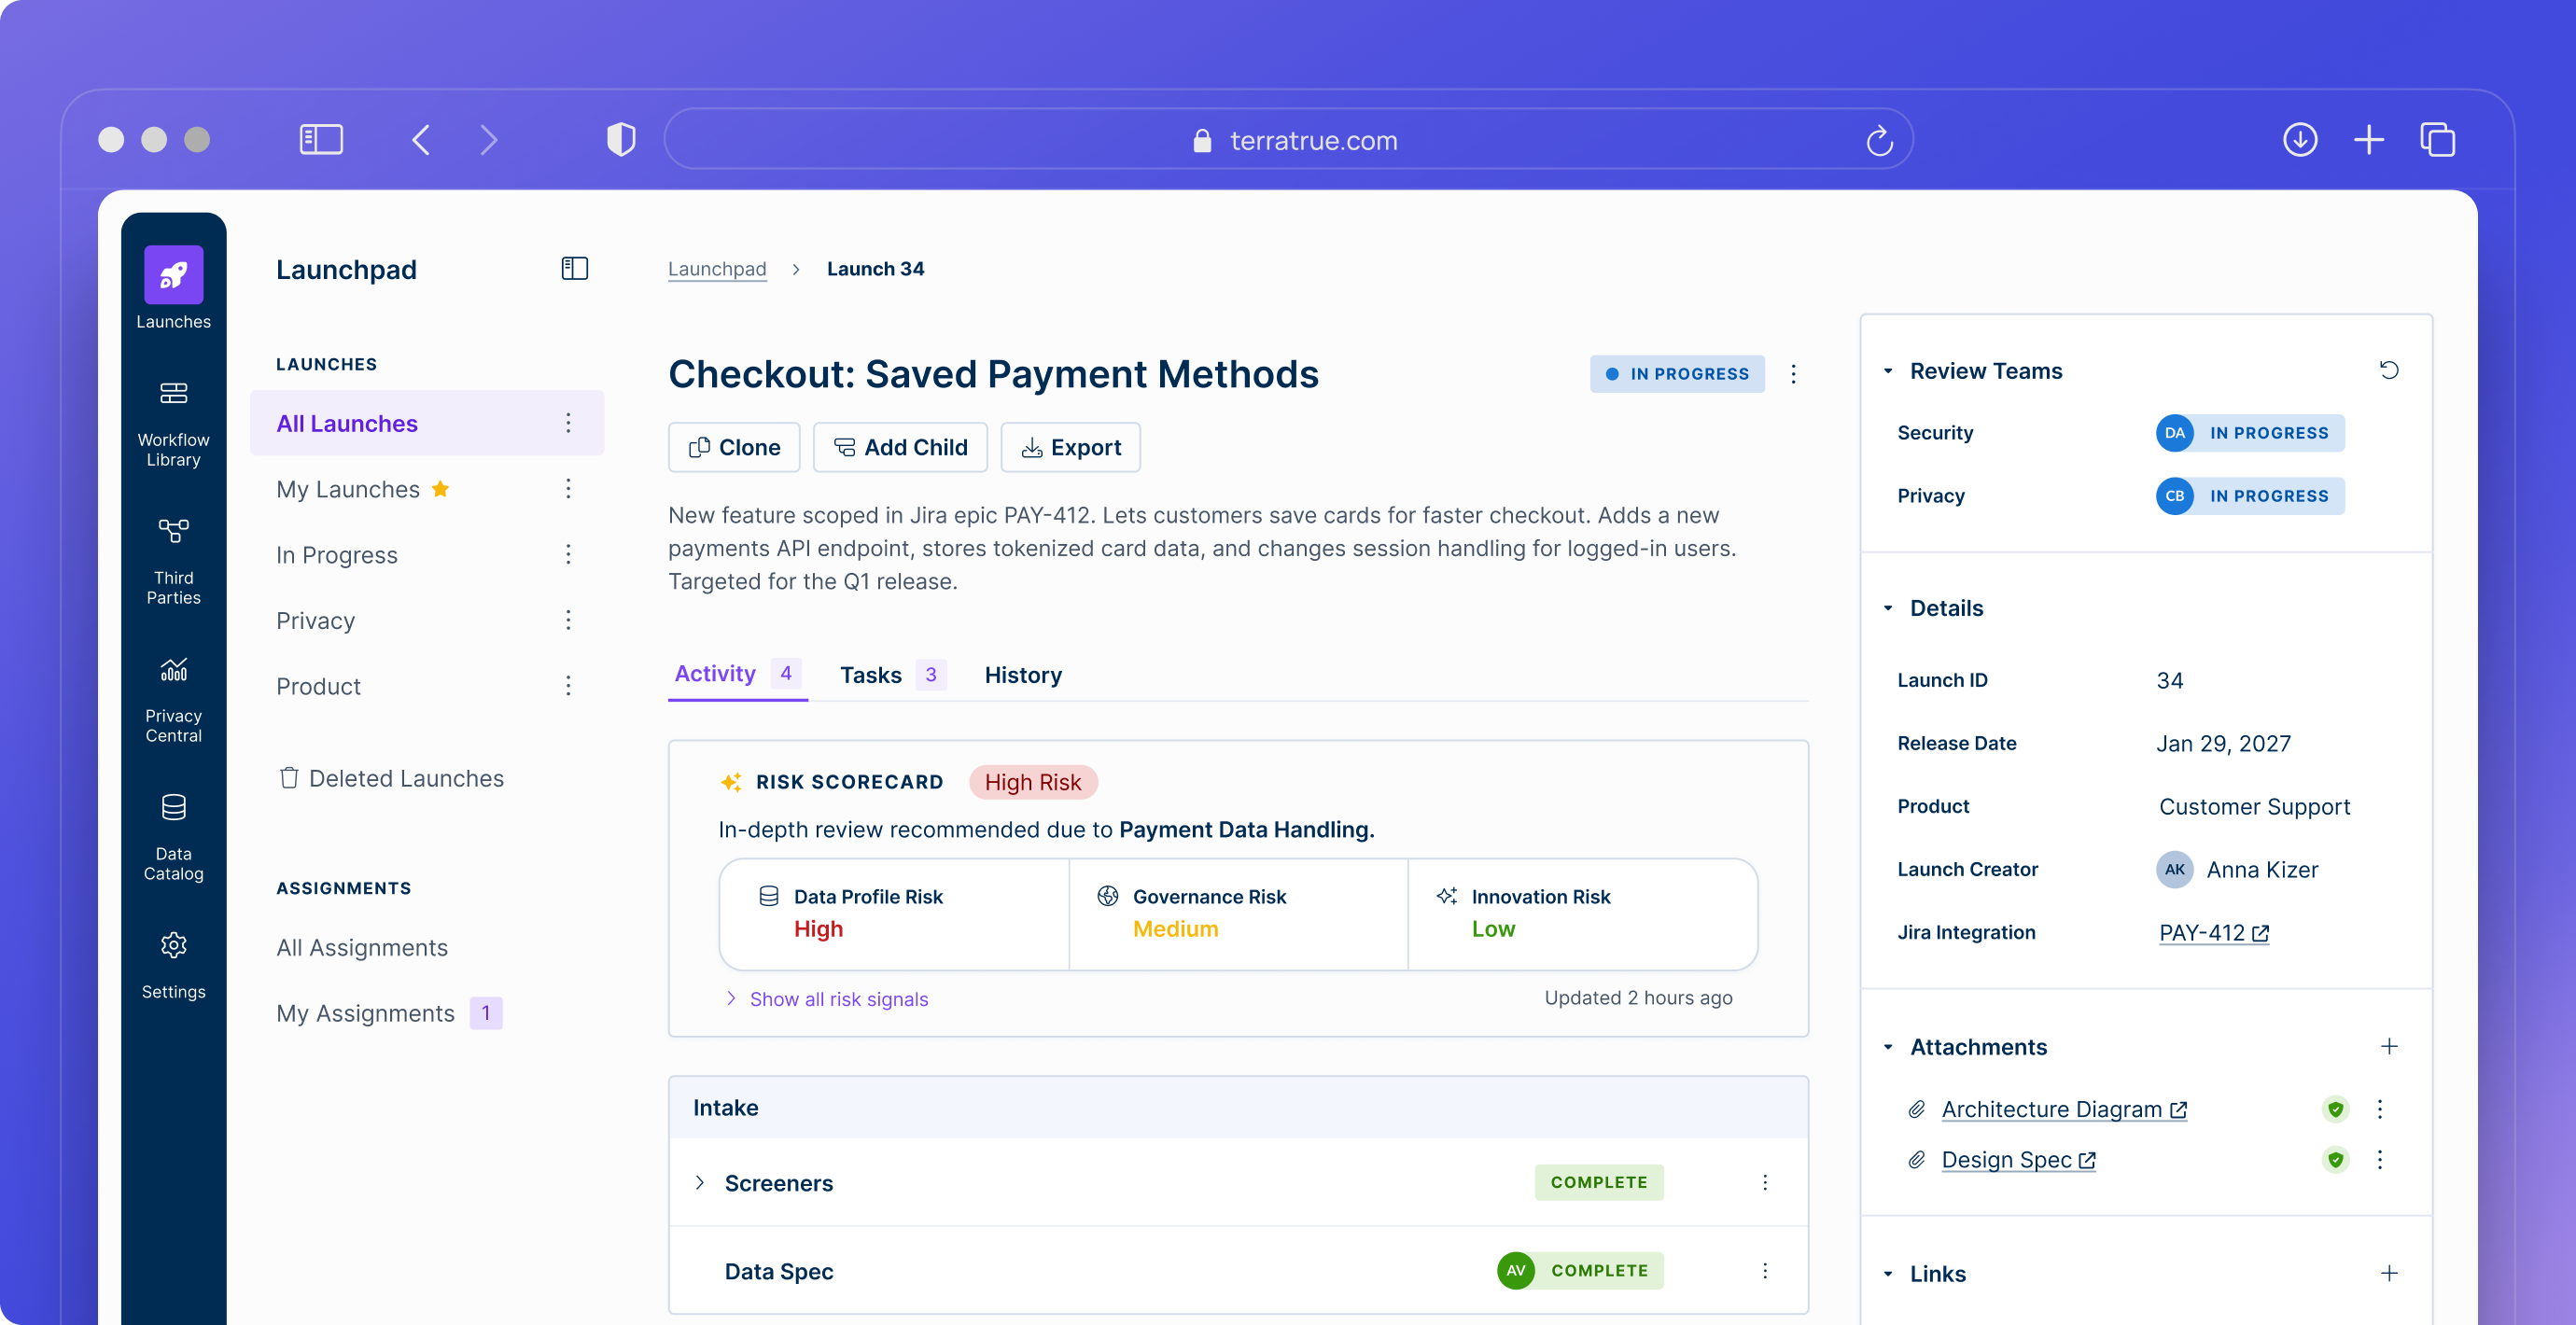
Web browser window open to terratrue.com showing a project dashboard for 'Checkout: Saved Payment Methods' marked In Progress. The description notes a new feature in Jira epic PAY-412 to save cards for faster checkout, using a new payments API, tokenizing card data, and session handling changes. Tabs show Activity with 4 items, Tasks 3, and History. A risk scorecard indicates High Risk and recommends in-depth review for Customer Data Access, with Data Profile Risk high, Governance Risk medium, and Innovation Risk low. Below, the Intake section lists Screeners marked Complete and Data Spec marked Complete with status icons.Screenshot of a web application interface showing a project dashboard on terratrue.com with navigation menu on the left including Launchpad, Workflow Library, Third Parties, Privacy Central, Data Catalog, and Settings. The main panel displays 'Checkout: Saved Payment Methods' project with tabs for Activity, Tasks, and History. There is a risk scorecard indicating 'High Risk' for Payment Data Handling with details on Data Profile Risk (High), Governance Risk (Medium), and Innovation Risk (Low). Sections show Intake with Screeners and Data Spec marked complete. The right sidebar lists Review Teams with security and privacy statuses as In Progress, project details including Launch ID 34, release date Jan 29, 2027, product Customer Support, launch creator Anna Kizer, Jira Integration, attachments, and links.

Make security part of the plan

Simple purple binoculars icon with two circular lenses connected by a bridge.
See every feature before it’s built
Security gets visibility the moment new work is scoped.
Purple bell icon with two curved lines on top representing ringing or notification.
Never miss a review
Reviews open automatically from Jira or Slack, with no one needing to remember to file.
Purple wrench icon with thick lines.
Get findings fixed, not filed
Findings land in the backlog of the team that owns the code.

One review, every domain

New features go through one intake in Jira or Slack, which brings in privacy, security, and AI reviewers when the risk calls for it.
Reviews Triggered at Scoping
The Jira epic opens the security review alongside it. No separate intake, and no ticket someone has to remember to file.
Connected Risk Domains
A single intake in Jira or Slack starts privacy assessments and alerts AppSec or AI teams when thresholds are met.
Risk Scorecard
Every launch is scored across risk categories, so AppSec sees what needs a real review.
Remediation in the Backlog
Findings become Jira tasks for the team that owns the code, with owners and due dates, tracked to closure in the review record.
SLA Tracking
Track reviews against launch completion targets so security is never the bottleneck.
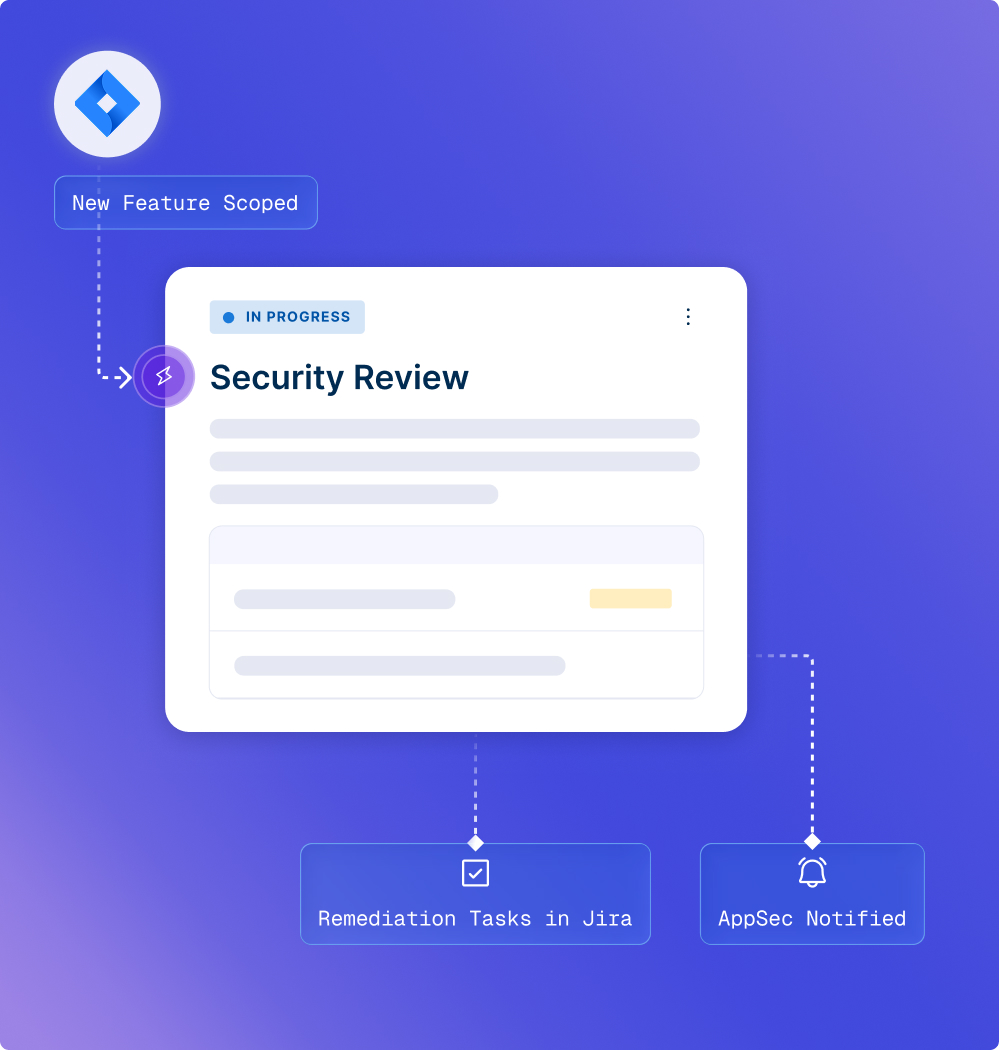
Diagram illustrating a workflow for a security review in progress on a software platform, linking new feature scoping to remediation tasks in Jira and AppSec notifications.

Every feature gets reviewed

A review opens as soon as a new intake is created in Jira or Slack.
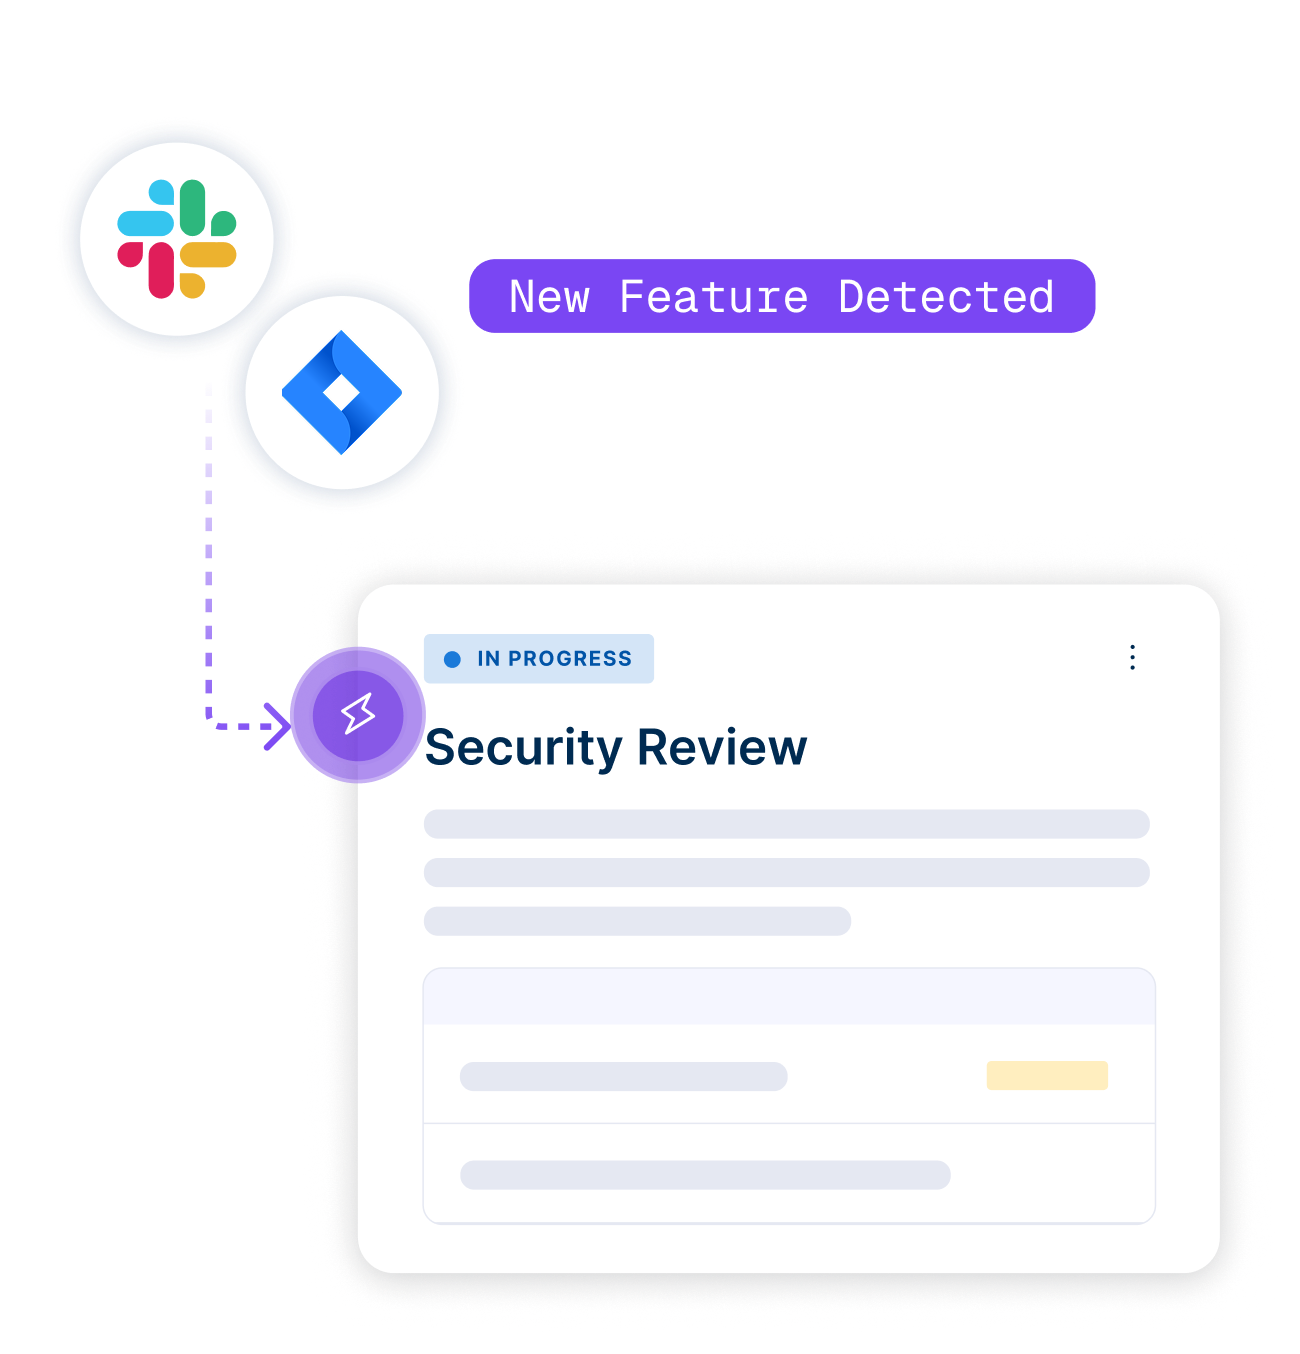
Illustration showing integration between Slack and Jira icons linked by a dotted arrow to a notification panel labeled 'New Feature Detected' and titled 'Security Review' with an 'In Progress' status.
Risk scorecard showing high risk for Data Profile and Governance, and low risk for Innovation, with respective icons for each category.

Effort goes where the risk is

Every launch is scored across risk categories, so AppSec knows what reviews need more diligence.

Findings get fixed, not forgotten

Remediation tickets land in the Jira backlog of the team that owns the code.
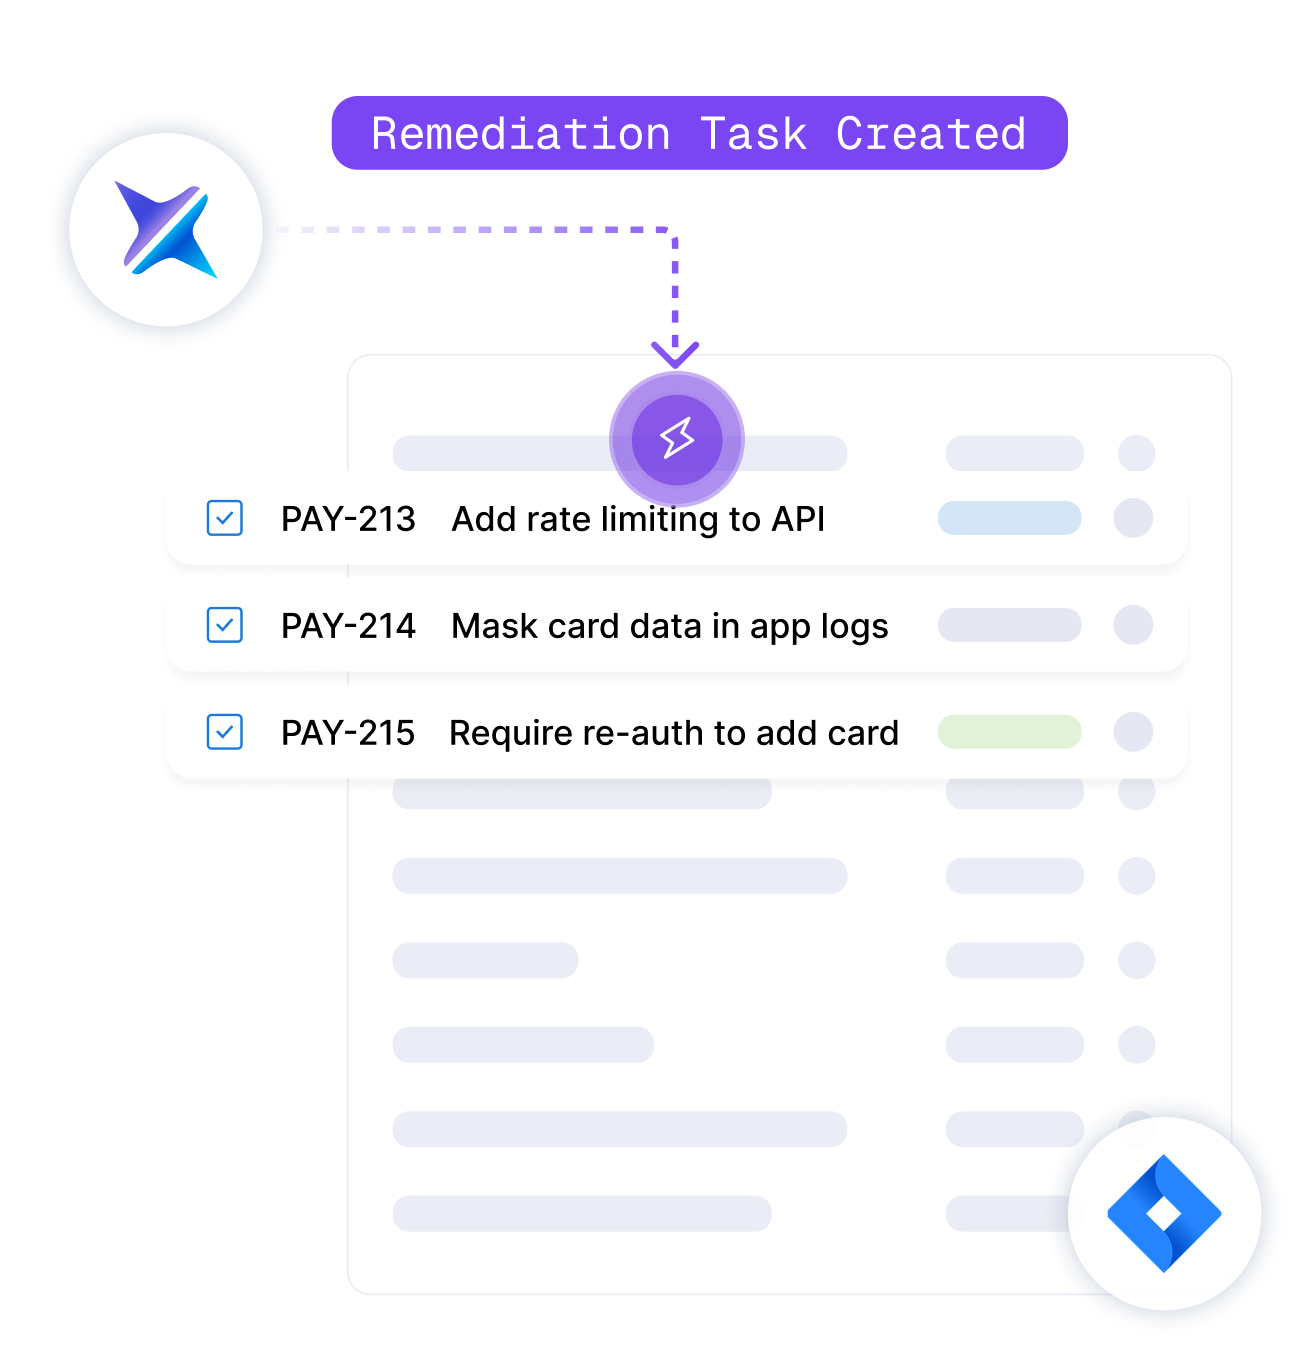
An interface showing a remediation task created notification with a list of three tasks: PAY-213 Add rate limiting to API, PAY-214 Mask card data in app logs, and PAY-215 Require re-auth to add card, each with a checked box. The tasks are linked by a dashed arrow to a lightning bolt icon and surrounded by two circular logos.
The word 'depop' in bold white lowercase letters on a purple gradient background.

“Tasks that previously took me 3-4 hours are now taking around 30-45 minutes.

And I'm able to clear Jira tickets much faster.”
— Esther Okeke / Senior Infosec Analyst

Works with tools you already use
Security FAQs

Placeholder
Does this replace our AppSec tools?

No, it’s the design review and intake layer. Findings go to your existing backlog. 

Can we use our own security questionnaire?

You can use TerraTrue’s security questionnaire templates as-is, modify them to fit your requirements, or create your own using a no-code workflow builder.

How do findings reach engineers?

As Jira tasks with owners and due dates.

Put security in the design doc, not the incident report.